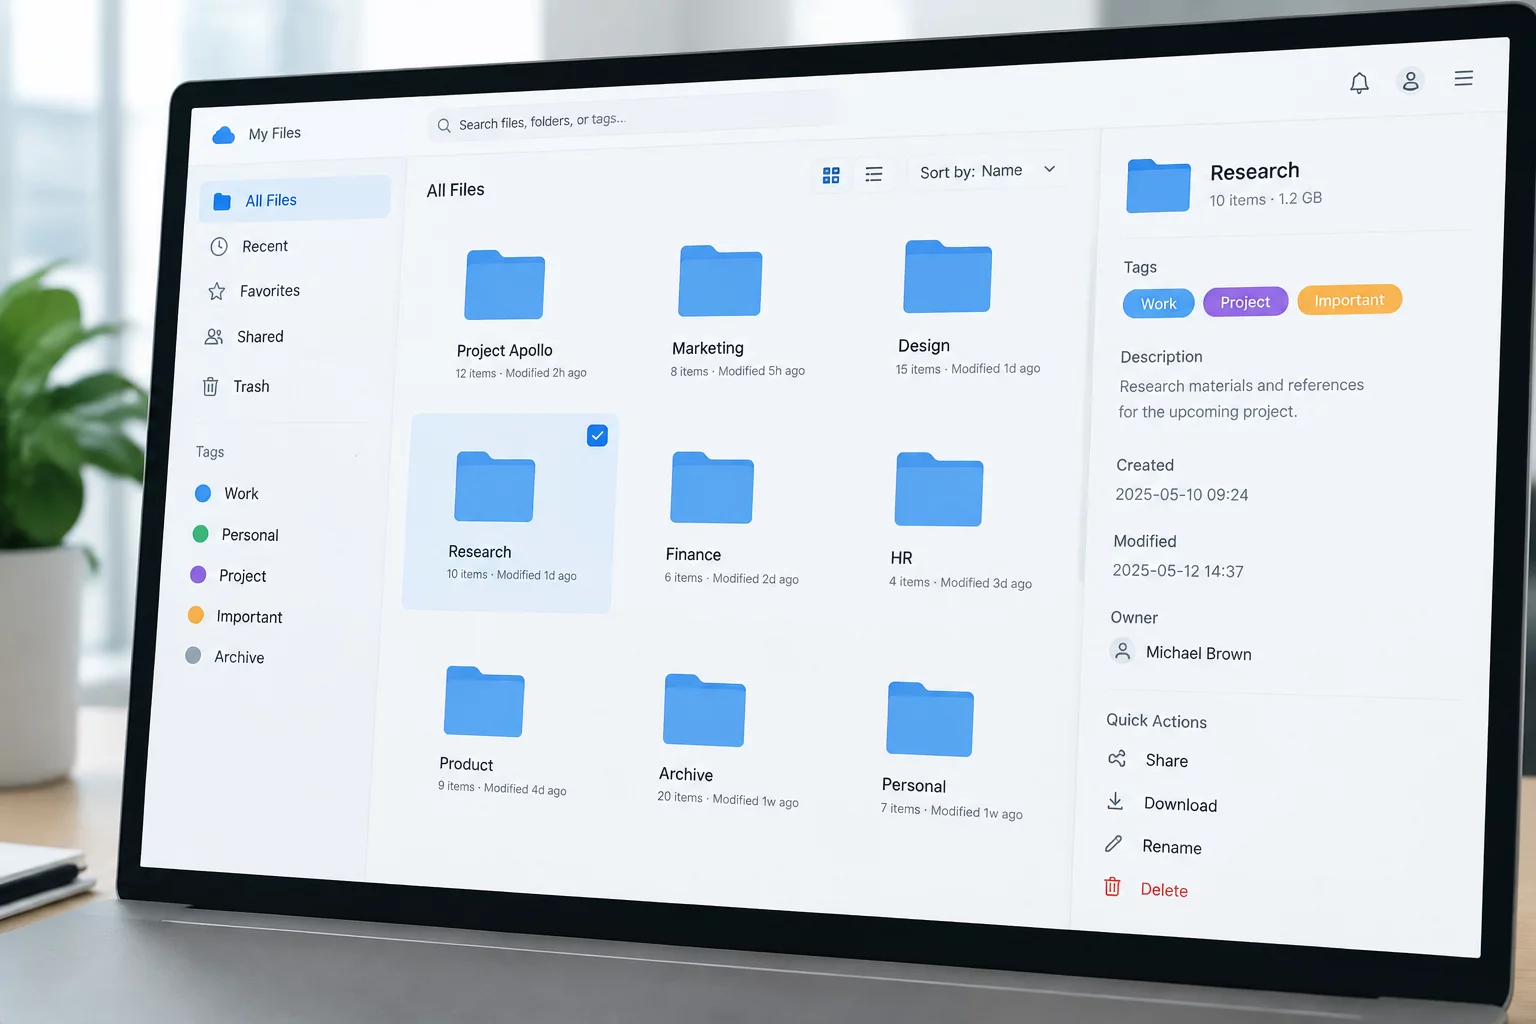
Uncontrolled shared drives and cloud workspaces naturally degenerate into unindexed dumps where duplicate versions and orphan assets consume storage budgets. Enterprise taxonomy standards establish rigid boundaries for naming conventions, nested depths, and access levels, ensuring every asset remains retrievable whether traversed via local file managers or queried through programmatic search APIs.
Structural Hierarchy and Namespace Division
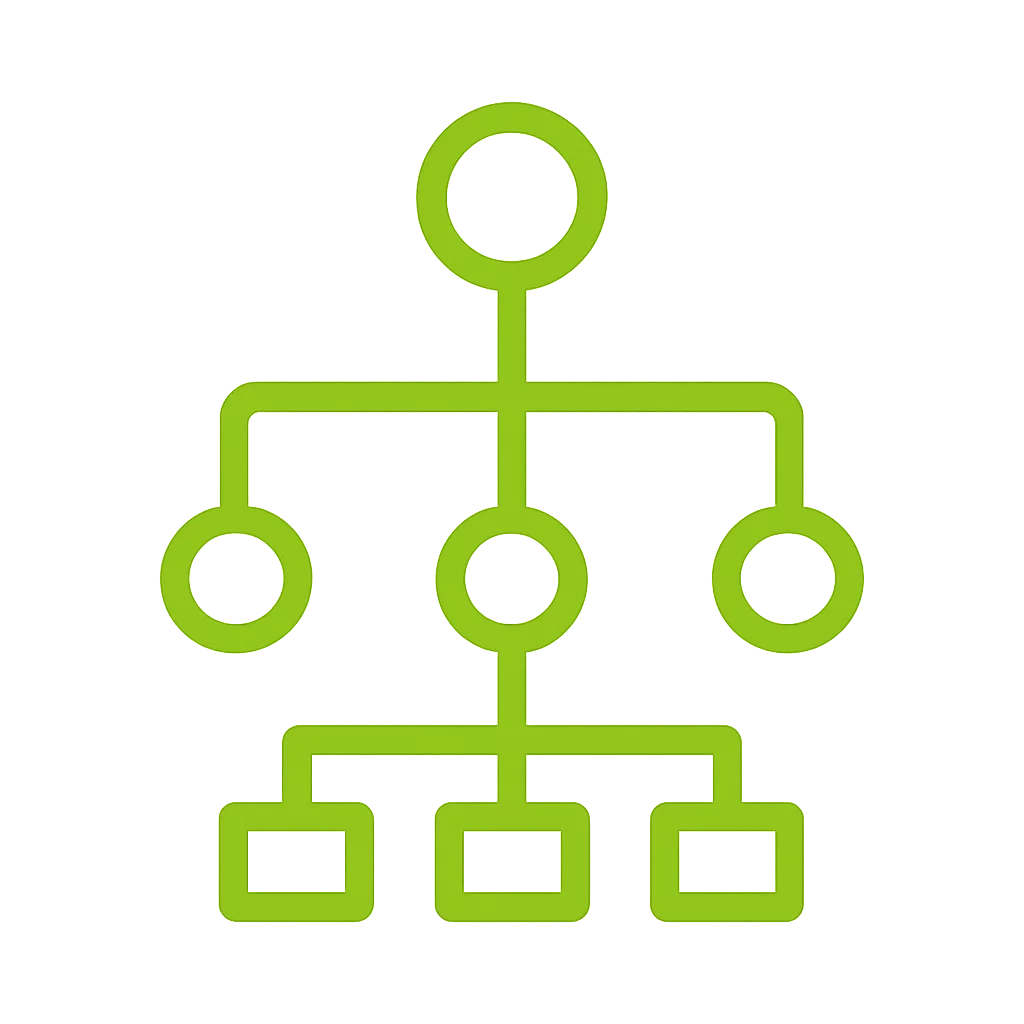
Modern directory classification separates volatile working spaces from immutable records. Teams frequently build overly deep directory trees under the false belief that granular categories simplify retrieval. In practice, directories extending beyond four nested levels trigger critical path length limit exceptions on legacy POSIX tools and degrade traversal speed during bulk synchronization operations.
Under this standard, top-level containers represent operational divisions or primary projects, followed by standardized functional stages such as specifications, source deliverables, and sign-offs. Individual file identifiers embed concise chronological tokens that allow deterministic lexical sorting regardless of host filesystem sorting algorithms.
- Strict four-tier directory nesting limit to eliminate path length overflow errors across operating systems
- ISO-8601 calendar date prefixing on file assets for automatic temporal ordering across client shells
- Automated manifest generation linking binary blobs with structured schema sidecars in JSON and YAML
A directory tree lacking unambiguous taxonomy boundaries inevitably decays into an unsearchable digital swamp within eighteen months of active collaboration.
Retention Lifecycle and Permission Boundaries
Standardizing physical folder locations directly governs lifecycle policies. By designating dedicated cold storage paths alongside daily scratch directories, retention daemons can systematically apply compression profiles and tier migration rules without inspecting individual payload headers. Assets tagged for multi-year compliance move to read-only partitions with cryptographic checksums recorded upon ingestion.
Access control inheritance benefits equally from predictable parent paths. Security groups map cleanly to departmental root collections, eliminating broken security permissions that frequently occur when nested subfolders inherit ad-hoc local privileges. When auditing directory health, automated crawl scripts flag non-compliant naming patterns, path depth violations, and stale files requiring archival.
Taxonomy Architecture Questions
While modern cloud buckets possess flat key-value spaces without nesting caps, team members frequently interact with file shares through local synchronizers or operating systems that enforce legacy 260-character total path caps. Restricting trees to four functional tiers prevents path truncation bugs and keeps terminal navigation rapid.
Draft documents belong exclusively within designated active scratch workspaces where version increments occur freely. Once approved, the document artifact transitions into a write-once archival path with checksum indexing, preventing revision drift in shared organizational libraries.
Enterprise standards place functional organizational units or persistent project codes at the root level, followed by lifecycle stage, with calendar dates applied as file prefixes. Date-first root trees scatter continuous project collateral across disconnected fiscal periods, causing fragmented audits.